Blog
Guides, case studies and news.
Practical security guides, training paths, case studies and news from the Kage team.
 Latest · Microsoft Sentinel
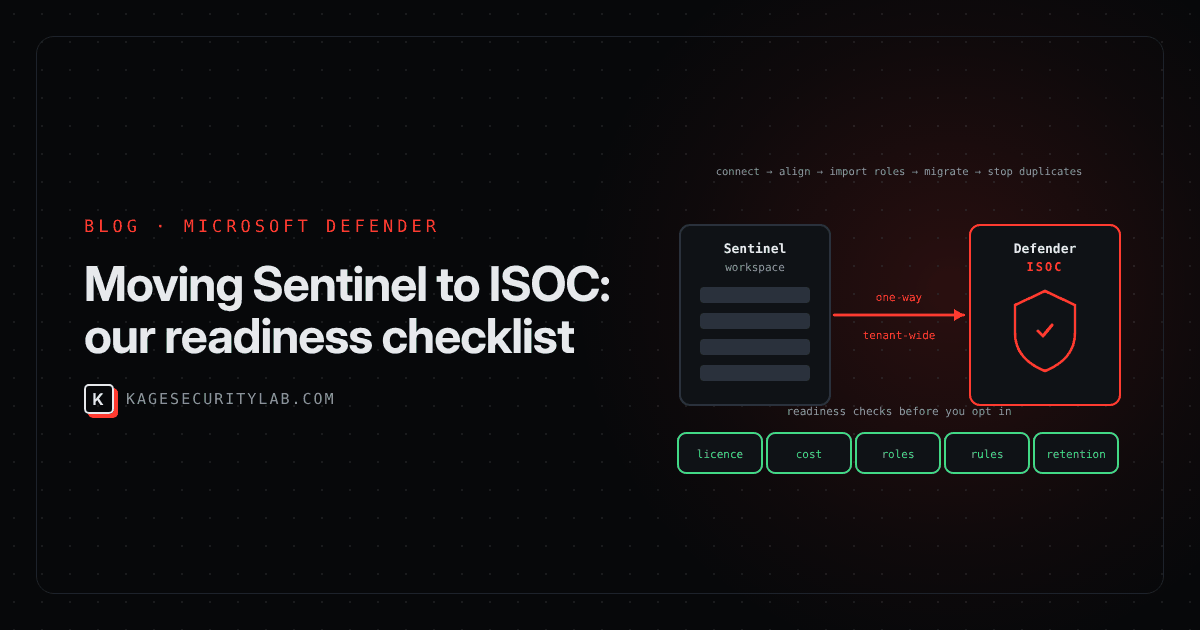
Moving Microsoft Sentinel to ISOC: our readiness checklist
ISOC brings Sentinel's SIEM into the Defender portal, but for existing Sentinel customers the switch is tenant-wide and cannot be undone. These are the five checks we run before we move a customer, the two queries behind them, and the order we use to avoid detection gaps.
Read the post
More from the lab
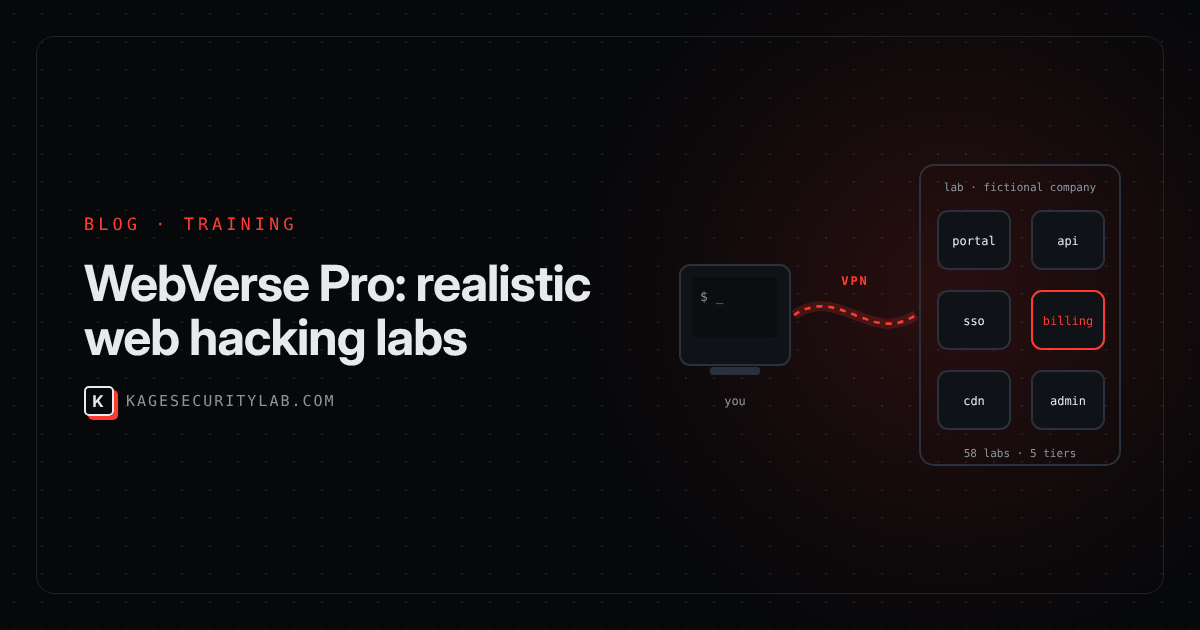 WebVerse Pro: realistic web hacking labs worth knowing about
A look at WebVerse Pro, a web security training platform where every lab is a full fictional company you attack over a private VPN: what it offers, who it suits, and how to get the most out of it.
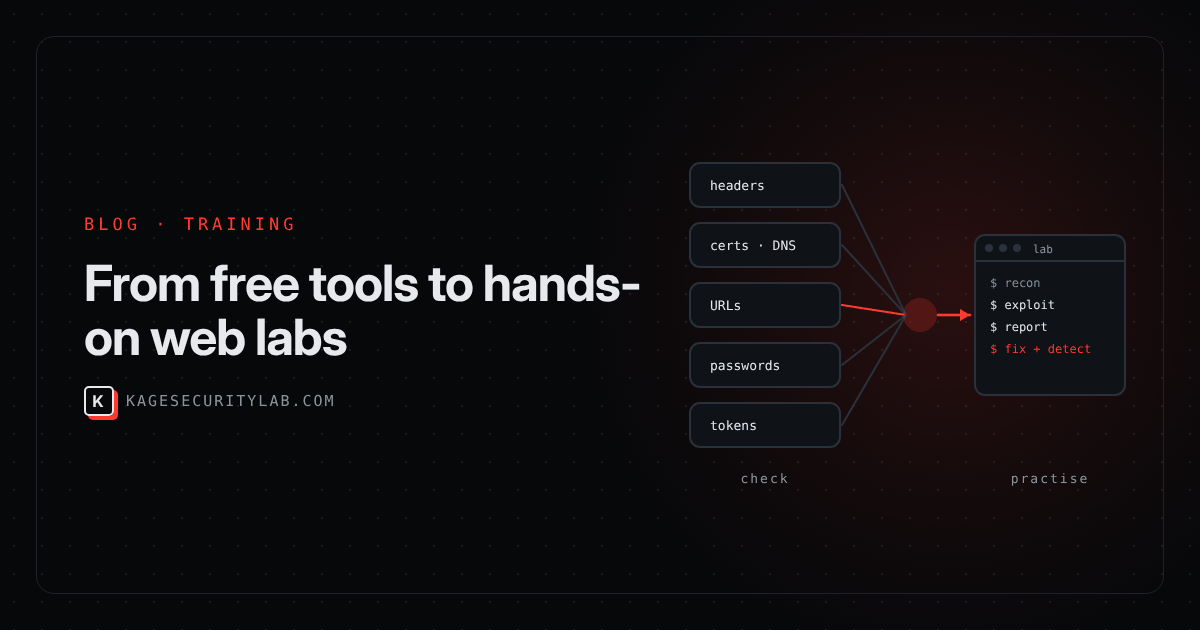 From our free tools to hands-on labs: a web security practice path
Each of our free checks shows a defender's view of a web weakness. Here is what an attacker does with the same signal, and where to practise it legally, tool by tool.
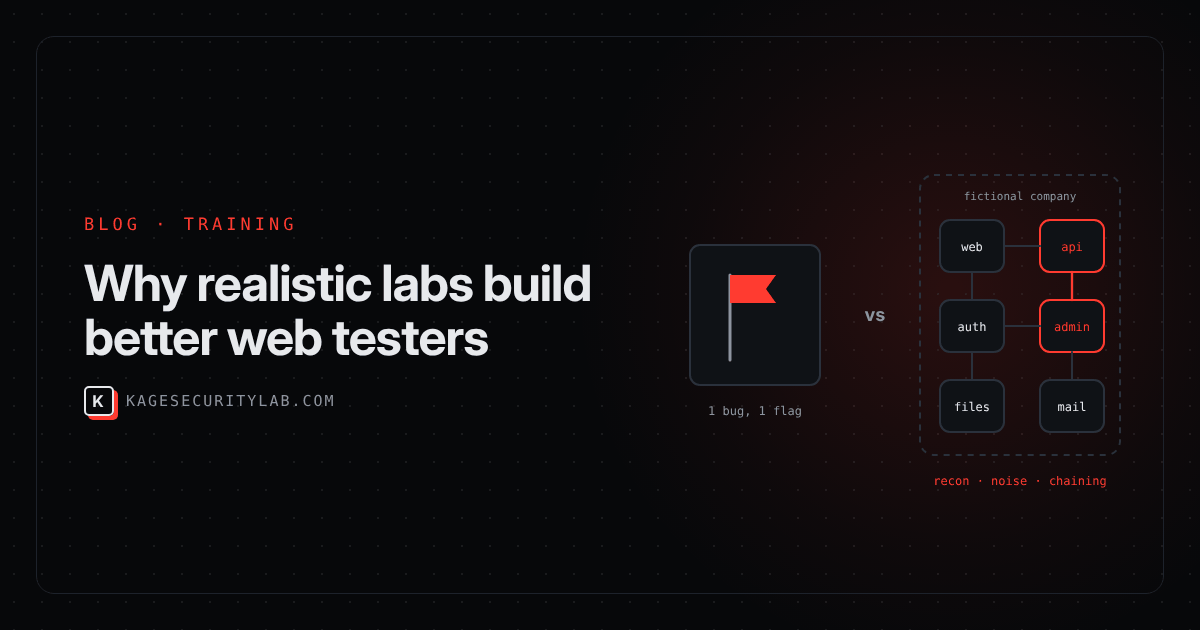 Why realistic labs build better web testers than isolated challenges
Single-bug challenges teach you what a vulnerability is. Full-environment labs teach you how to find one in an application that was not built to be hacked. What each is good for, and a training loop that uses both.
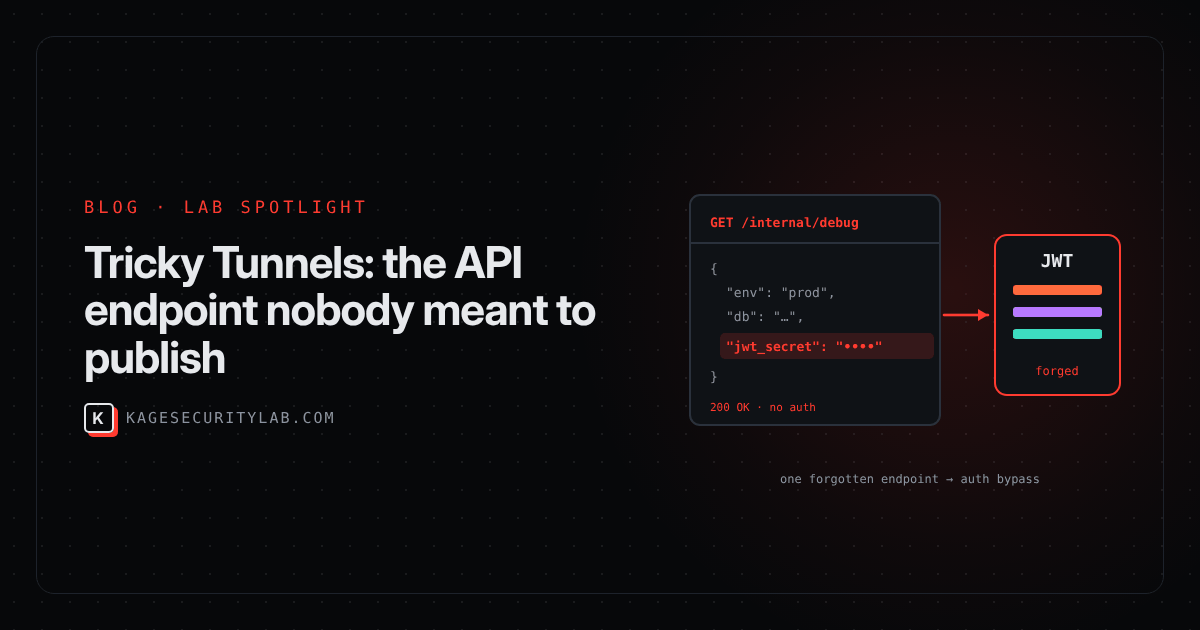 Lab spotlight: Tricky Tunnels and the API endpoint nobody meant to publish
A WebVerse Pro lab built around one of the most common API findings we report: an internal debug endpoint left reachable, leaking a token-signing secret. What it teaches, and the defender checklist that prevents it. Spoiler-light.
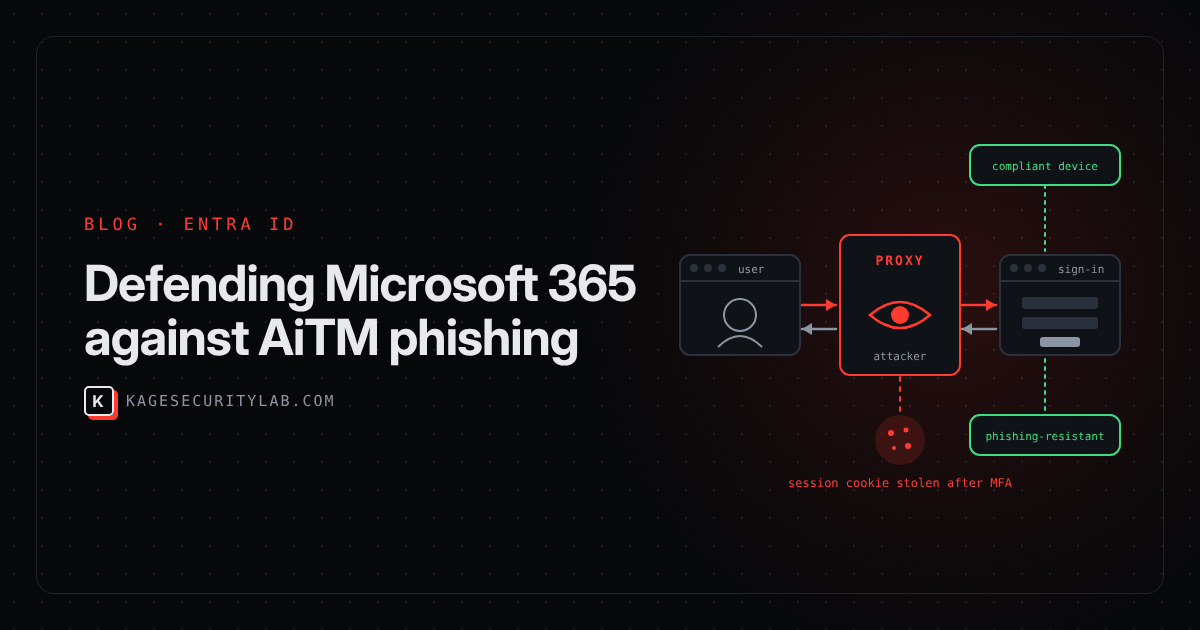 Defending Microsoft 365 against adversary-in-the-middle phishing
AiTM kits proxy the real Microsoft sign-in page and steal the session cookie after MFA completes. Here is what actually stops them.
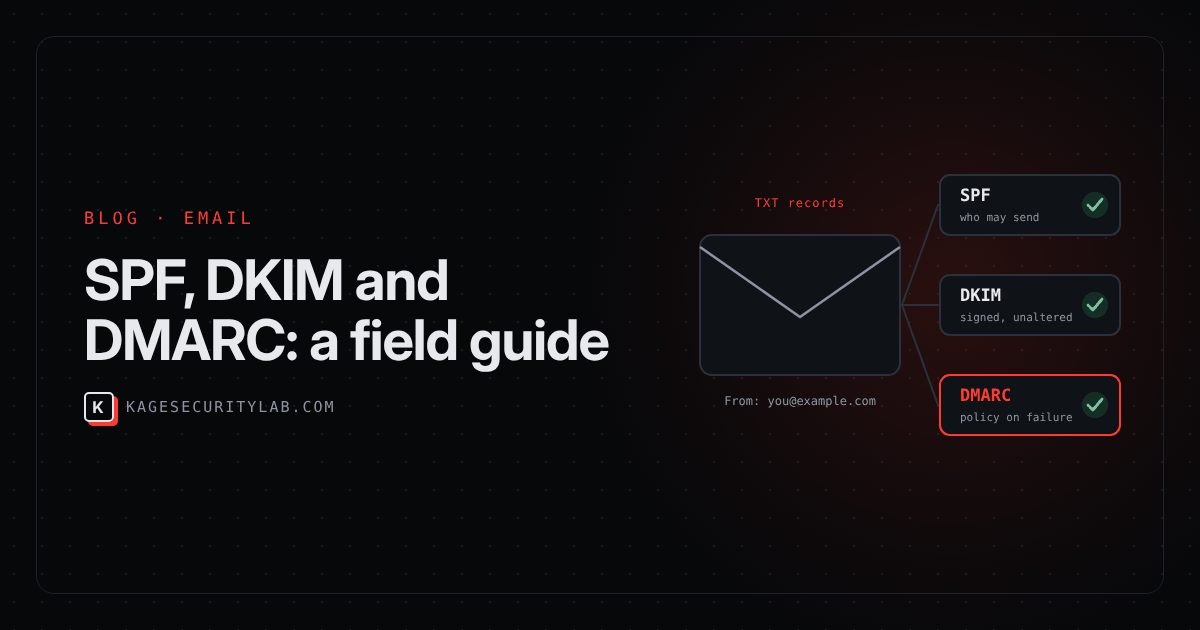 SPF, DKIM and DMARC: a field guide
Three DNS records decide whether anyone can send email as your domain. What each one does, the common mistakes, and a safe rollout path.
No posts match.